


Prepare for your exam certification with our FCP_FSM_AN-7.2 Certified Fortinet
Free Fortinet FCP_FSM_AN-7.2 Exam 2026 Practice Materials Collection
Fortinet FCP_FSM_AN-7.2 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 15
What are two required components of a rule? (Choose two.)
- A. Clear policy
- B. Detection Technology
- C. Exception policy
- D. Subpattern
Answer: B,D
Explanation:
A Subpattern defines the specific conditions or event patterns the rule is designed to detect, and the Detection Technology specifies the type of detection logic (e.g., real-time, historical). Both are essential for a rule to function in FortiSIEM.
NEW QUESTION # 16
How does FortiSIEM update the incident table if a performance rule triggers repeatedly?
- A. FortiSIEM changes the incident status to Repeated, and updates the Last Seen timestamp.
- B. FortiSIEM generates a new incident each time the rule triggers, and updates the First Seen and Last Seen timestamps.
- C. FortiSIEM updates the Incident Count value and Last Seen timestamp.
- D. FortiSIEM generates a new incident based on the Rule Frequency value, and updates the First Seen and Last Seen timestamps.
Answer: C
Explanation:
When a performance rule triggers repeatedly, FortiSIEM updates the existing incident by incrementing the Incident Count and refreshing the Last Seen timestamp. This avoids flooding the incident table with duplicates while still tracking repeated occurrences.
NEW QUESTION # 17
What can you use to send data to FortiSIEM for user and entity behavior analytics (UEBA)?
- A. FortiSIEM worker
- B. SNMP
- C. FortiSIEM agent
- D. SSH
Answer: C
Explanation:
The FortiSIEM agent can be used to send detailed endpoint data such as user activity and process behavior to FortiSIEM, which is essential for performing User and Entity Behavior Analytics (UEBA).
NEW QUESTION # 18
What must you configure to apply ZTNA tags from FortiSIEM to devices in FortiClient EMS?
- A. Syslog connection to FortiSIEM from FortiGate firewalls
- B. API connection from FortiSIEM to FortiClient EMS
- C. API connection from FortiClient EMS to FortiSIEM
- D. Syslog connection to FortiGate firewalls from FortiSIEM
Answer: B
NEW QUESTION # 19
Which two settings must you configure to allow FortiSIEM to apply tags to devices in FortiClient EMS? (Choose two.)
- A. FortiSIEM API credentials defined on FortiEMS\
- B. Remediation script configured
- C. FortiEMS API credentials defined on FortiSIEM
- D. ZTNA tags defined on FortiSIEM
Answer: A,C
Explanation:
To allow FortiSIEM to apply tags to devices in FortiClient EMS, FortiEMS API credentials must be defined on FortiSIEM to enable communication with EMS, and FortiSIEM API credentials must be defined on FortiEMS to allow EMS to accept tagging instructions from FortiSIEM. This bidirectional API trust is essential for tag application.
NEW QUESTION # 20
Refer to the exhibit.
According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?
- A. FortiSIEM fails to the integration policy, because no policy is defined.
- B. FortiSIEM performs all selected actions.
- C. FortiSIEM runs the remediation script, because that takes precedence over all other options.
- D. FortiSIEM sends an email, because that is first on the list.
Answer: B
Explanation:
When an associated rule triggers, FortiSIEM performs all selected actions in the automation policy. In this case, it will send an email/SMS/webhook, run the remediation script, invoke the integration policy (even if none is currently defined), and create a case. All checked actions are executed.
NEW QUESTION # 21
Which two attributes can you not select together in the Group By and Display Fields? (Choose two.)
- A. Event Reporting Time
- B. Reporting IP
- C. Raw Event Log
- D. Source IP
- E. Destination IP
Answer: C,E
NEW QUESTION # 22
Refer to the exhibit.
As shown in the exhibit, why are some of the fields highlighted in red?
- A. Unique values cannot be grouped B.
- B. The Event Receive Time attribute is not available for logs.
- C. No RAW Event Log attribute information is available.
- D. The attribute COUNT(Matched Events) is an invalid expression.
Answer: A
Explanation:
The fields are highlighted in red because unique values such as Event Receive Time and Raw Event Log cannot be used in group-by operations. Grouping requires aggregatable or consistent values across events, while these fields are unique to each event, making them incompatible for grouping.
NEW QUESTION # 23
Refer to the exhibit.
If you group the events by User and Count attributes, how many results will FortiSIEM display?
- A. Five
- B. Three
- C. Two
- D. One
- E. Six
Answer: A
Explanation:
Grouping by User and Count yields five unique pairs: (Mike,4), (Bob,3), (Alice,2), (Bob,6), (Mike,5).
NEW QUESTION # 24
Refer to the exhibit.
An analyst wants the rule shown in the exhibit to trigger when three failed login attempts occur within three minutes.
What should the values be for the condition time window and aggregate count?
- A. Time window 180 seconds, aggregate count 2
- B. Time window 90 seconds, aggregate count 2
- C. Time window 90 seconds, aggregate count 3
- D. Time window 180 seconds, aggregate count 3
Answer: D
Explanation:
To detect three failed login attempts within three minutes, you must set the aggregate count to 3 in the subpattern and the time window to 180 seconds in the rule condition. This ensures the rule triggers only if three or more failed logins occur in that timeframe.
NEW QUESTION # 25
What can you use to send data to FortiSIEM for user and entity behavior analytics (UEBA)?
- A. FortiSIEM worker
- B. SNMP
- C. FortiSIEM agent
- D. SSH
Answer: C
Explanation:
The FortiSIEM agent can be used to send detailed endpoint data such as user activity and process behavior to FortiSIEM, which is essential for performing User and Entity Behavior Analytics (UEBA).
NEW QUESTION # 26
Refer to the exhibit.
A FortiSIEM device is receiving syslog events from a FortiGate firewall. The FortiSIEM analyst is trying to search the raw event logs for the last two hours that contain the keyword "udp".
However, they are getting no results from the search, which they know should be available.
Based on the filter shown in the exhibit, why are there no search results?
- A. The analyst selected AND in the Next column. This is the wrong Boolean operator.
- B. The analyst selected = in the Operator column. That is the wrong operator.
- C. The keyword is case sensitive. Instead of typing udp in the Value field, the analyst should type UDP.
- D. The Time Range value should be set to Real-Time.
Answer: B
Explanation:
The operator is set to "=", which performs an exact match on the entire raw event log, not a substring search. To find logs that contain the keyword "udp", the analyst should use the CONTAIN operator instead. This will return all logs where "udp" appears anywhere in the raw log message.
NEW QUESTION # 27
Refer to the exhibit.
What happens when an analyst clears an incident generated by a rule containing the automation policy shown in the exhibit?
- A. An email is sent to the SOC manager.
- B. A notification is sent to the SOC manager dashboard.
- C. The remediation script is run.
- D. No notification is sent.
Answer: D
Explanation:
The automation policy has the option "Do not notify when an incident is cleared manually" enabled. Therefore, when an analyst manually clears an incident, no notification or automation action is triggered.
NEW QUESTION # 28
Refer to the exhibit.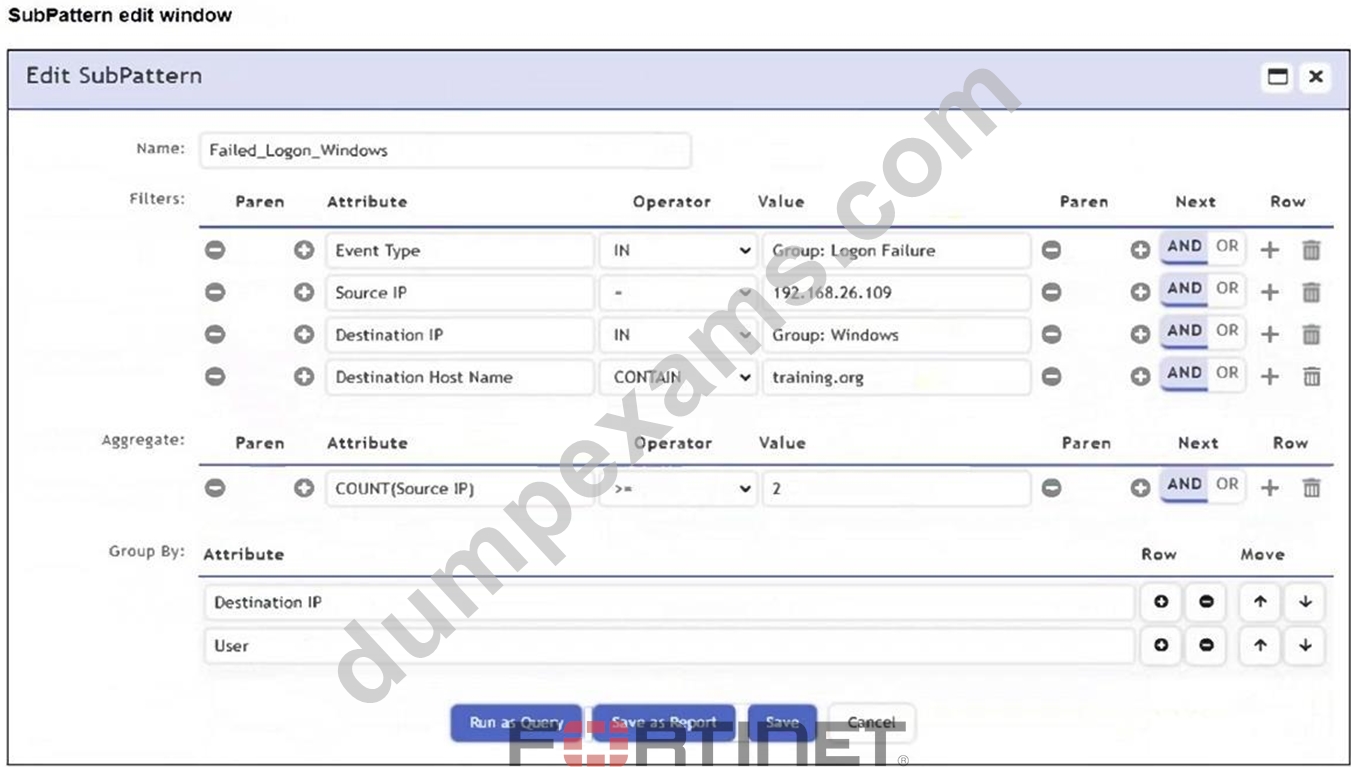
An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab.
What is wrong with the rule conditions?
- A. The Destination Host Name value is not fully qualified.
- B. The Group By attributes restricts which events are counted.
- C. The Aggregate attribute is too restrictive.
- D. The Event Type refers to a CMDB lookup and should be an Event lookup.
Answer: B
Explanation:
The Group By attributes - Destination IP and User - cause the aggregation (COUNT(Source IP) >= 2) to apply within each unique combination of those groupings. This restricts the count calculation and can prevent the rule from triggering incidents, even if matching events exist in the Analytics tab.
NEW QUESTION # 29
Which running mode takes the most time to perform machine learning tasks?
- A. Regression
- B. Local auto
- C. Local
- D. Forecasting
Answer: C
Explanation:
In Local mode, FortiSIEM performs machine learning tasks using the full dataset without optimization shortcuts, making it the most time-consuming mode compared to Local Auto, Forecasting, or Regression.
NEW QUESTION # 30
Which analytics search can be used to apply a user and entity behavior analytics (UEBA) tag to an event for a failed login by the user JSmith?
- A. Username NOT END WITH jsmith
- B. Username CONTAIN smit
- C. User = smith
- D. User IS jsmith
Answer: D
Explanation:
The correct syntax to match an exact username in FortiSIEM analytics search is User IS jsmith.
This ensures that the UEBA tag is applied only when the event is specifically tied to the user
"jsmith", which is required for accurate behavioral analytics.
NEW QUESTION # 31
Refer to the exhibit.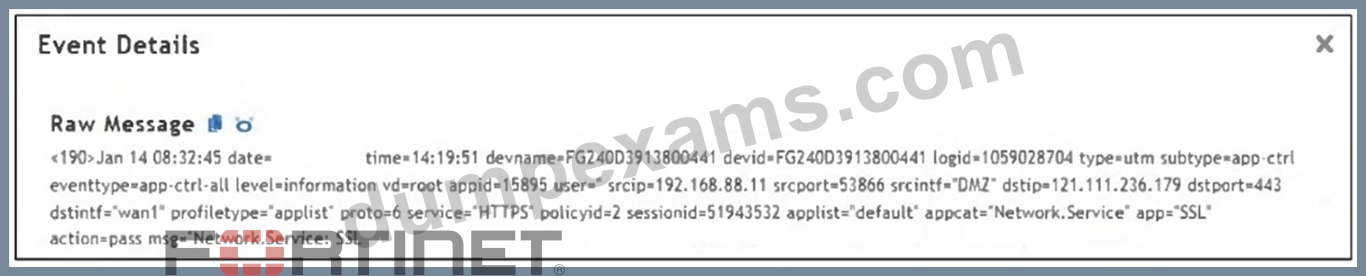
Which value would you expect the FortiSIEM parser to use to populate the Application Name field?
- A. applist
- B. SSL
- C. wan1
- D. Network.Service
Answer: B
Explanation:
The Application Name field in FortiSIEM is typically populated using the value of the app field in the raw log. In this event, app="SSL", so "SSL" is the expected application name parsed by FortiSIEM.
NEW QUESTION # 32
What are the five categories of incidents on FortiSIEM?
- A. Devices, users, high risk, other, and low risk
- B. Performance, other, availability, security, and change
- C. Security, change, high risk, low risk, and other
- D. Performance, other, devices, high risk, and low risk
Answer: B
NEW QUESTION # 33
Refer to the exhibit. Which section contains settings that determine which attribute associations are used to trigger an incident?
- A. Group By
- B. Name
- C. Filters
- D. Aggregate
Answer: A
NEW QUESTION # 34
Refer to the exhibit.
An analyst is trying to identify an issue using an expression based on the Expression Builder settings shown in the exhibit; however, the error message shown in the exhibit indicates that the expression is invalid.
What is the correct syntax to create an expression that generates a total count of matched events?
- A. COUNT(Matched Events)
- B. Matched Events COUNT()
- C. (COUNT) Matched Events
- D. Matched Events (COUNT)
Answer: A
Explanation:
The correct syntax is COUNT(Matched Events) - with proper capitalization and spacing - to generate a total count of matched events. The error in the exhibit likely stems from a formatting issue (e.g., lowercase count() or incorrect spacing), not the logical structure of the expression.
NEW QUESTION # 35
Refer to the exhibit.
An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add a Destination Host Name as an incident attribute.
What must be changed to allow the analyst to select Destination Host Name as an attribute?
- A. The Destination Host Name must be set as an aggregate item in a subpattern.
- B. The Destination Host Name must be added as an Event type in the FortiSIEM.
- C. The Destination Host Name must be selected as a Triggered Attribute.
- D. The Destination IP Event Attribute must be removed.
Answer: C
Explanation:
For an attribute like Destination Host Name to be used in the incident title, it must first be included in the Triggered Attributes list. Only attributes listed there are available for substitution in the title template (e.g., $destIpAddr, $srcIpAddr).
NEW QUESTION # 36
Refer to the exhibit.
Which value would you expect the FortiSIEM parser to use to populate the Application Name field?
- A. applist
- B. SSL
- C. wan1
- D. Network.Service
Answer: B
Explanation:
The Application Name field in FortiSIEM is typically populated using the value of the app field in the raw log. In this event, app="SSL", so "SSL" is the expected application name parsed by FortiSIEM.
NEW QUESTION # 37
When using user and entity behavior analytics (UEBA) on FortiSIEM, what must you use to dynamically supply a list of IP addresses to a FortiGate device for blocking purposes?
- A. Watchlists
- B. SCP
- C. Lookup tables
- D. API Connection
Answer: A
NEW QUESTION # 38
Refer to the exhibit.
The configuration shown in the exhibit is incorrect.
What must you change to allow this configuration to be successfully applied to FortiSIEM?
- A. The Train factor must be 70% or greater.
- B. Only one AVG type field must be selected under Fields to use for Prediction.
- C. Run Mode must be set to ML.
- D. The selection in Fields to use for Prediction and Field to Predict must match.
Answer: C
Explanation:
The Run Mode is set to Local, which is not valid for training machine learning models in FortiSIEM. To apply this configuration correctly, the Run Mode must be set to ML, which enables proper model training and prediction using selected fields.
NEW QUESTION # 39
Refer to the exhibit.
What will happen when a device being analyzed by the machine learning configuration shown in the exhibit has a consistently high memory utilization?
- A. FortiSIEM will lower the CPU utilization trigger requirement for CPU utilization.
- B. FortiSIEM will update the regression tables for memory utilization, and average sent and received bytes.
- C. FortiSIEM will update the model with a higher memory utilization average value.
- D. FortiSIEM will trigger an incident for high memory utilization.
Answer: C
Explanation:
In the configuration shown, FortiSIEM uses Memory Util, Sent Bytes, and Received Bytes as input features to predict CPU Utilization via a regression model. If a device shows consistently high memory utilization, the model will incorporate that into its training data and update itself with a higher average value for memory utilization, influencing future CPU utilization predictions.
NEW QUESTION # 40
......
Pass Fortinet FCP_FSM_AN-7.2 Actual Free Exam Q&As Updated Dump: https://passguide.dumpexams.com/FCP_FSM_AN-7.2-vce-torrent.html